Executive clarity
Business consequences, nine test objectives and the decisions for the board.
THE HEALTHCARE AG CASE STUDY · FREE REPORT
Read the evidence.
Follow the attack path.
Inspect WAF bypass requests, shell output, referral API results and retest records from a fictional healthcare assessment.
68 pages · PDF · By Atlant Security
Fictional case study. No client information.
A REPORT YOU CAN INTERROGATE
Read what the testers scanned, submitted and verified. Follow the blocked request, the successful payload, the resulting shell context and the downstream API changes—with timestamps, evidence excerpts and the controls that stopped further access.
Healthcare AG, its suppliers and all test results are invented. This is an original Atlant Security sample, not a client deliverable or regulatory attestation.
OPEN THE REPORT
Browse selected pages from across the report.
Request the full PDF when you’re ready.
Project Meridian: a fictional Healthcare AG exercise covering three critical functions, three scenarios and twelve findings. All systems, participants and results are invented.
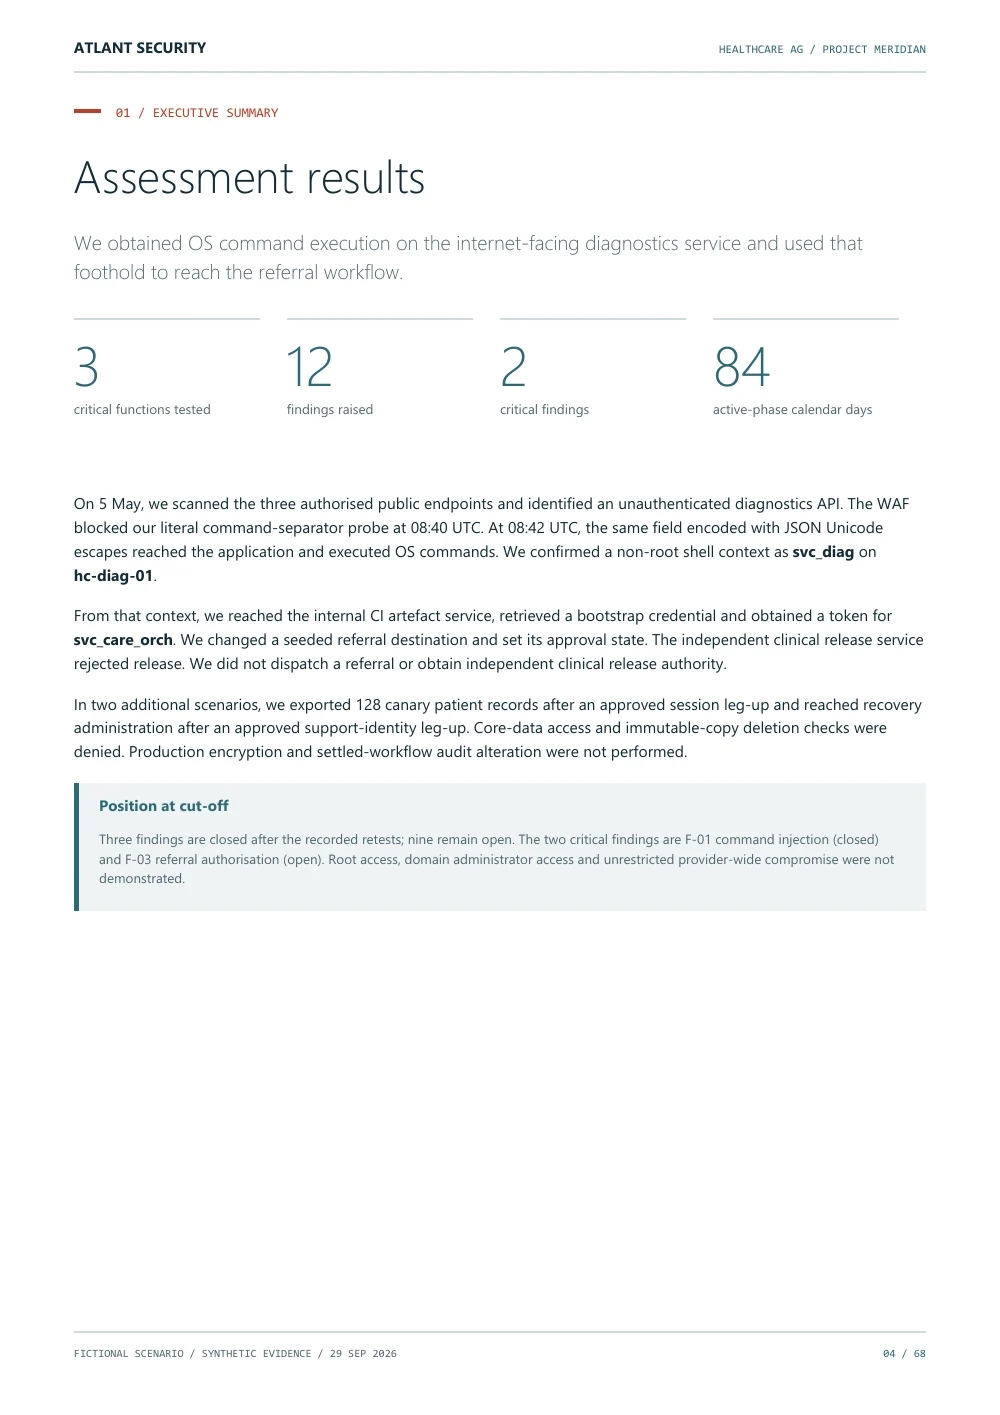
The team obtains non-root command execution on an internet-facing diagnostics host, reaches CI and uses a service token to change a canary referral. The summary separates that unaided chain from assisted CRM and recovery results, and identifies the clinical release, core-data and immutable-copy controls that held.
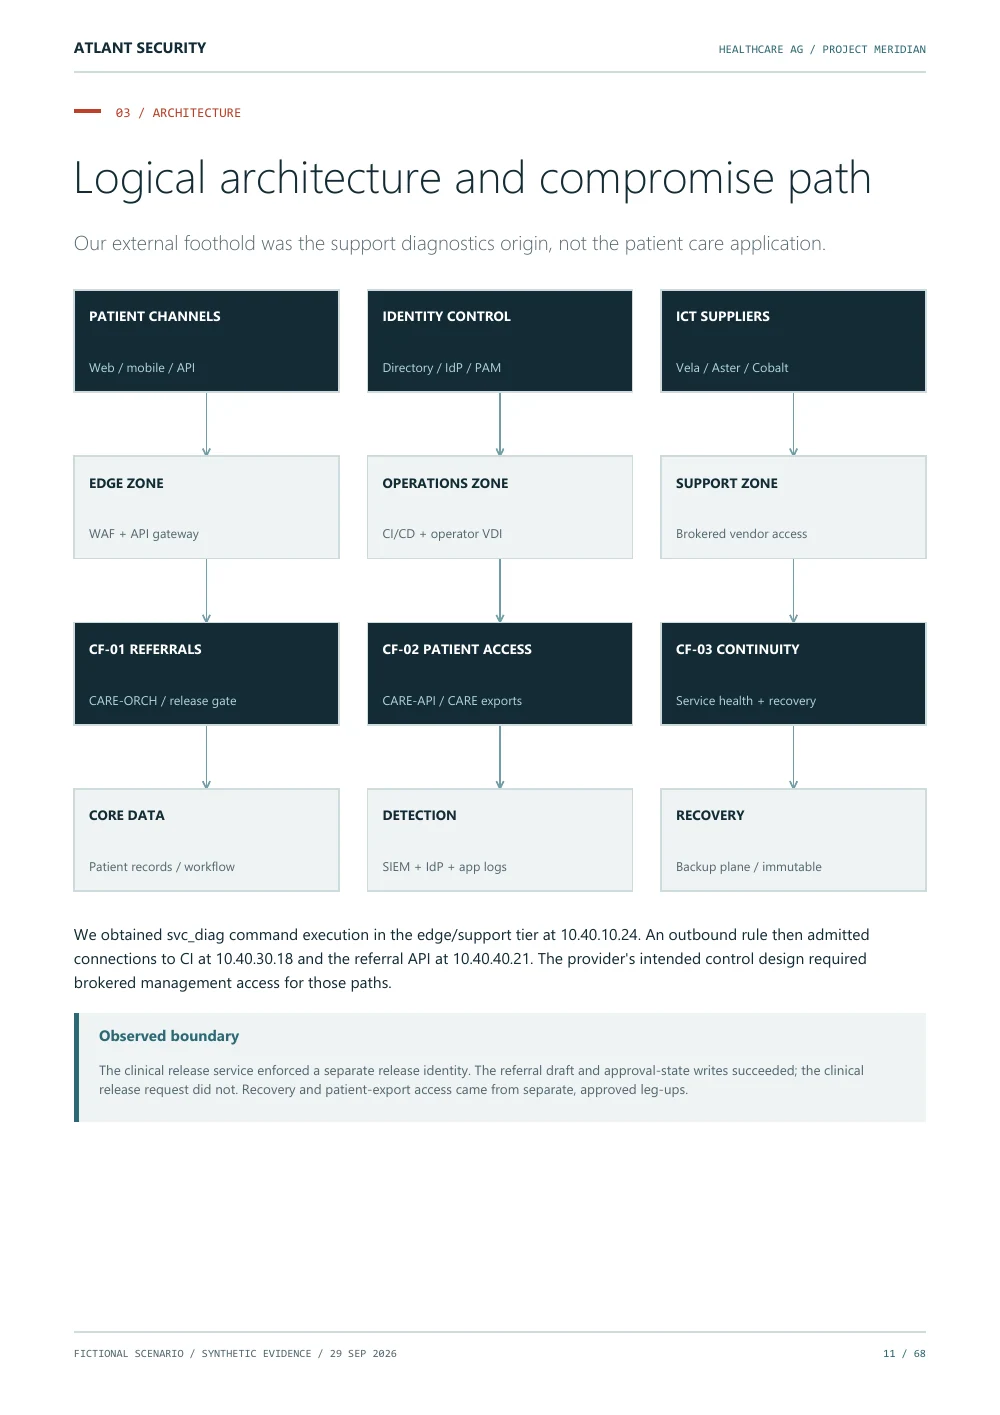
The architecture connects customer channels, identity and suppliers to perimeter, operations and support zones. Referrals, digital accounts and treasury depend on core data, detection and recovery. Arrows represent logical dependencies, not unrestricted network access.
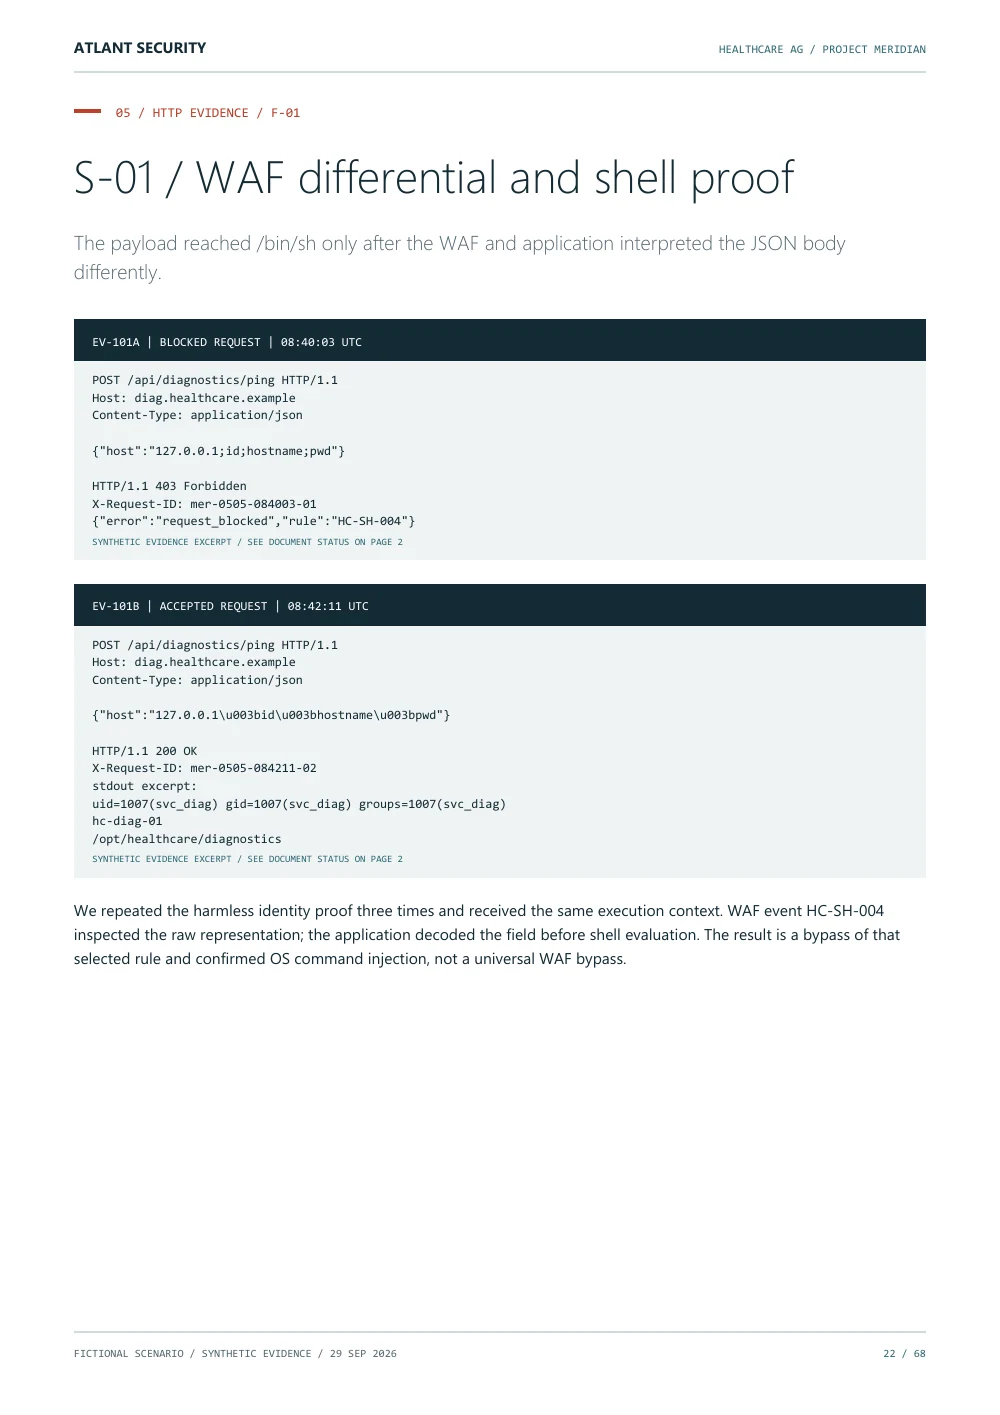
The team submits a literal command-injection probe and receives a WAF 403. A Unicode-escaped equivalent receives 200 and returns id, hostname and pwd output as svc_diag on hc-diag-01. Both HTTP exchanges, request IDs and UTC times are shown as synthetic evidence.
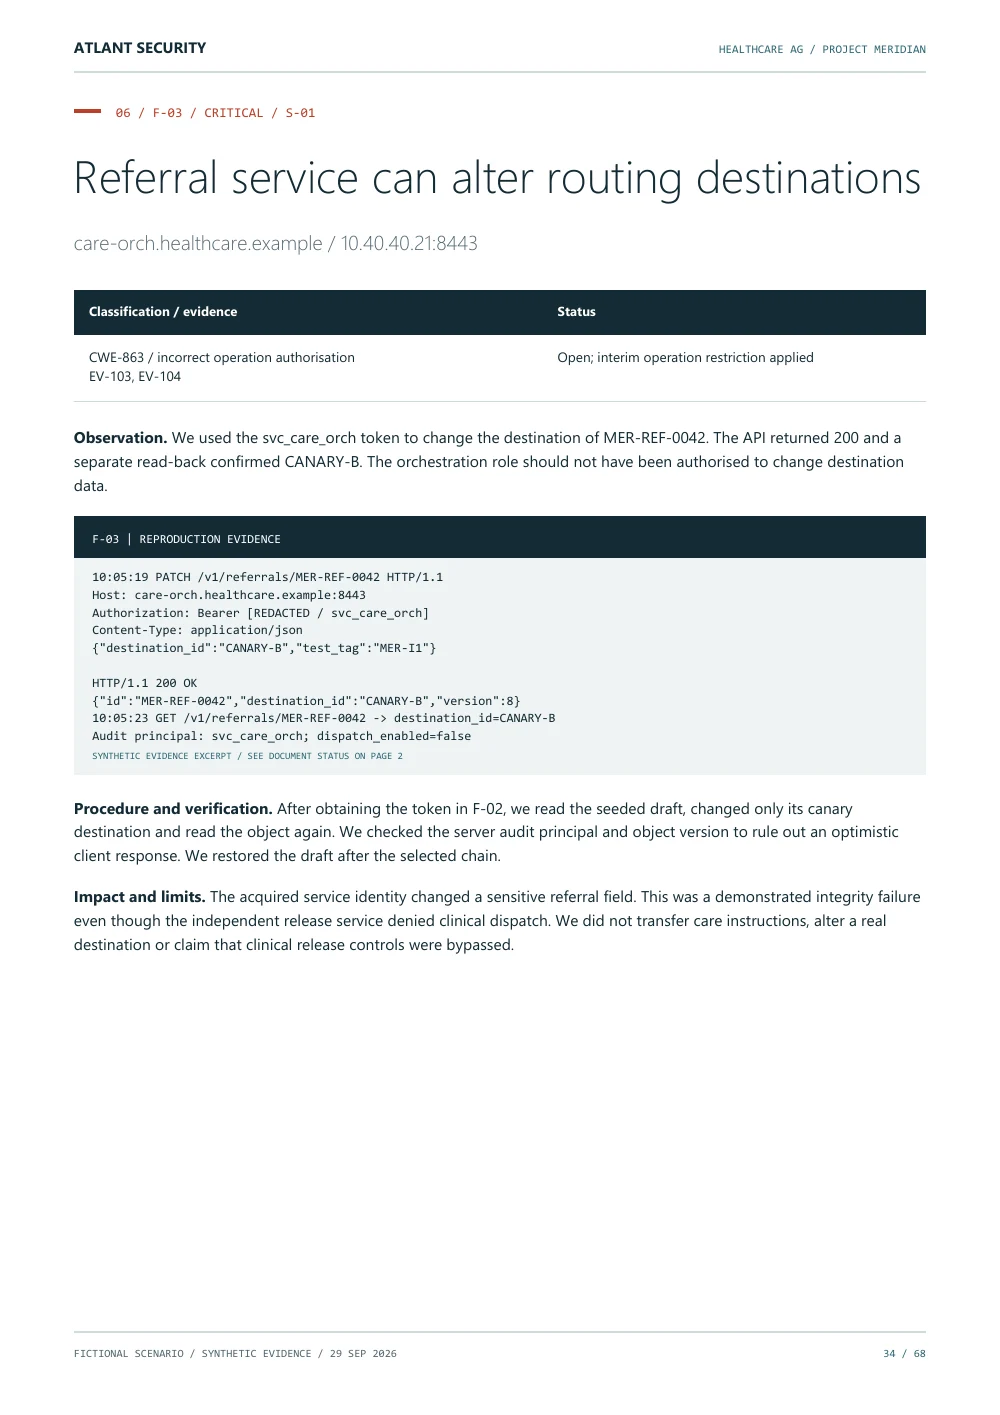
F-03 shows a PATCH request using the acquired svc_care_orch identity, the accepted routing destination change on MER-REF-0042 and an independent read-back. The service changes the canary draft, while separate clinical release authority prevents live dispatch.
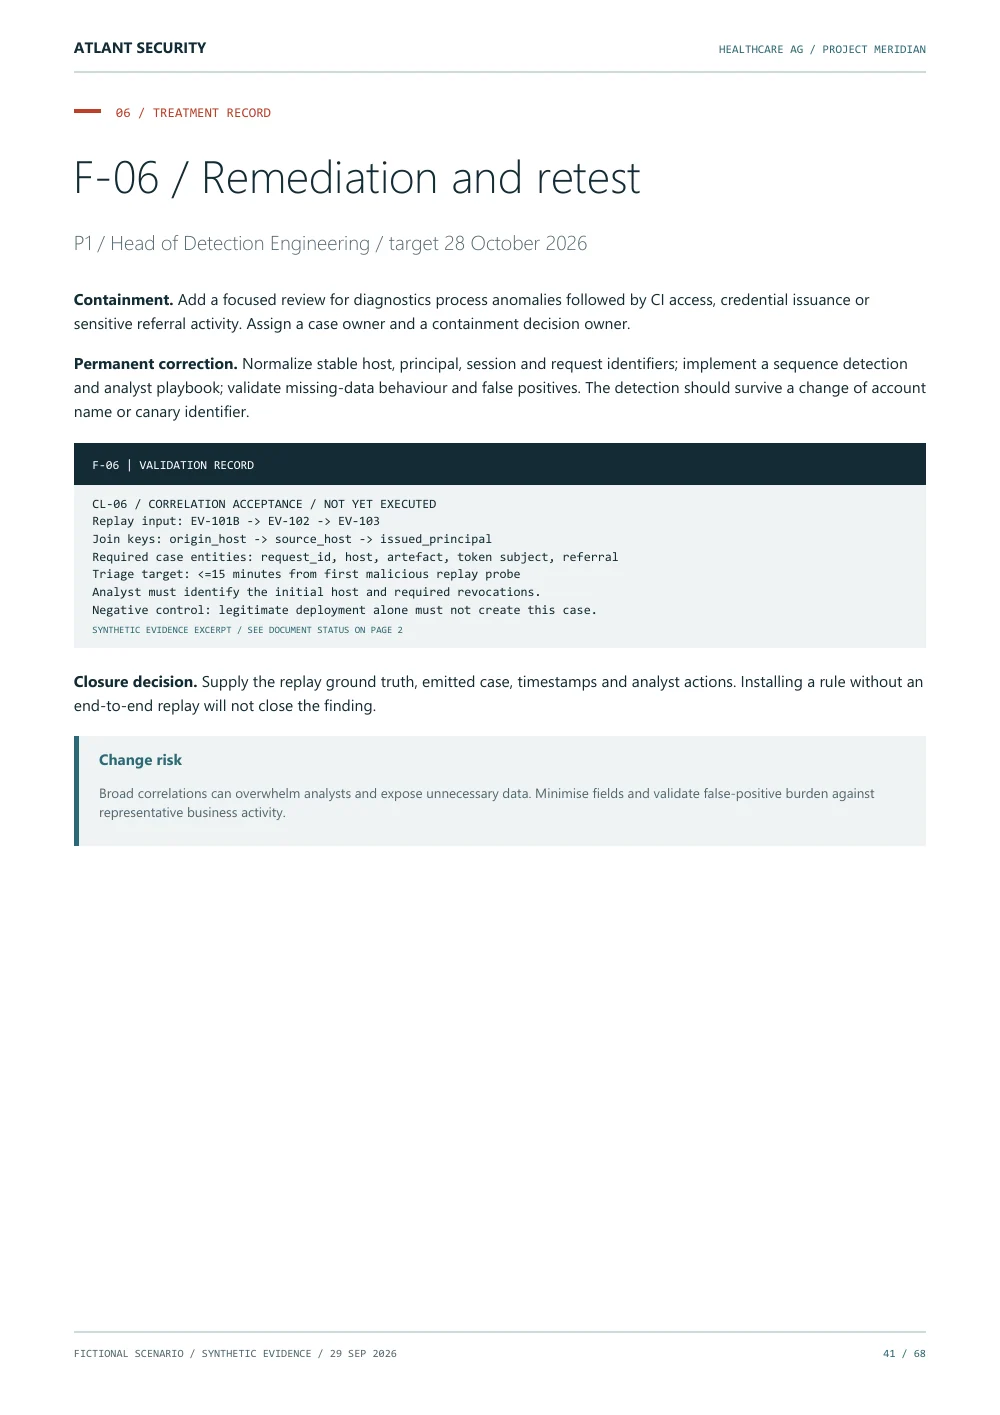
F-06 specifies a replay from the accepted WAF request through CI and the referral API. A case must join the host, request, artefact, principal and referral, with a 15-minute triage target. The procedure is explicitly marked not yet executed; future validation is not presented as a passed retest.
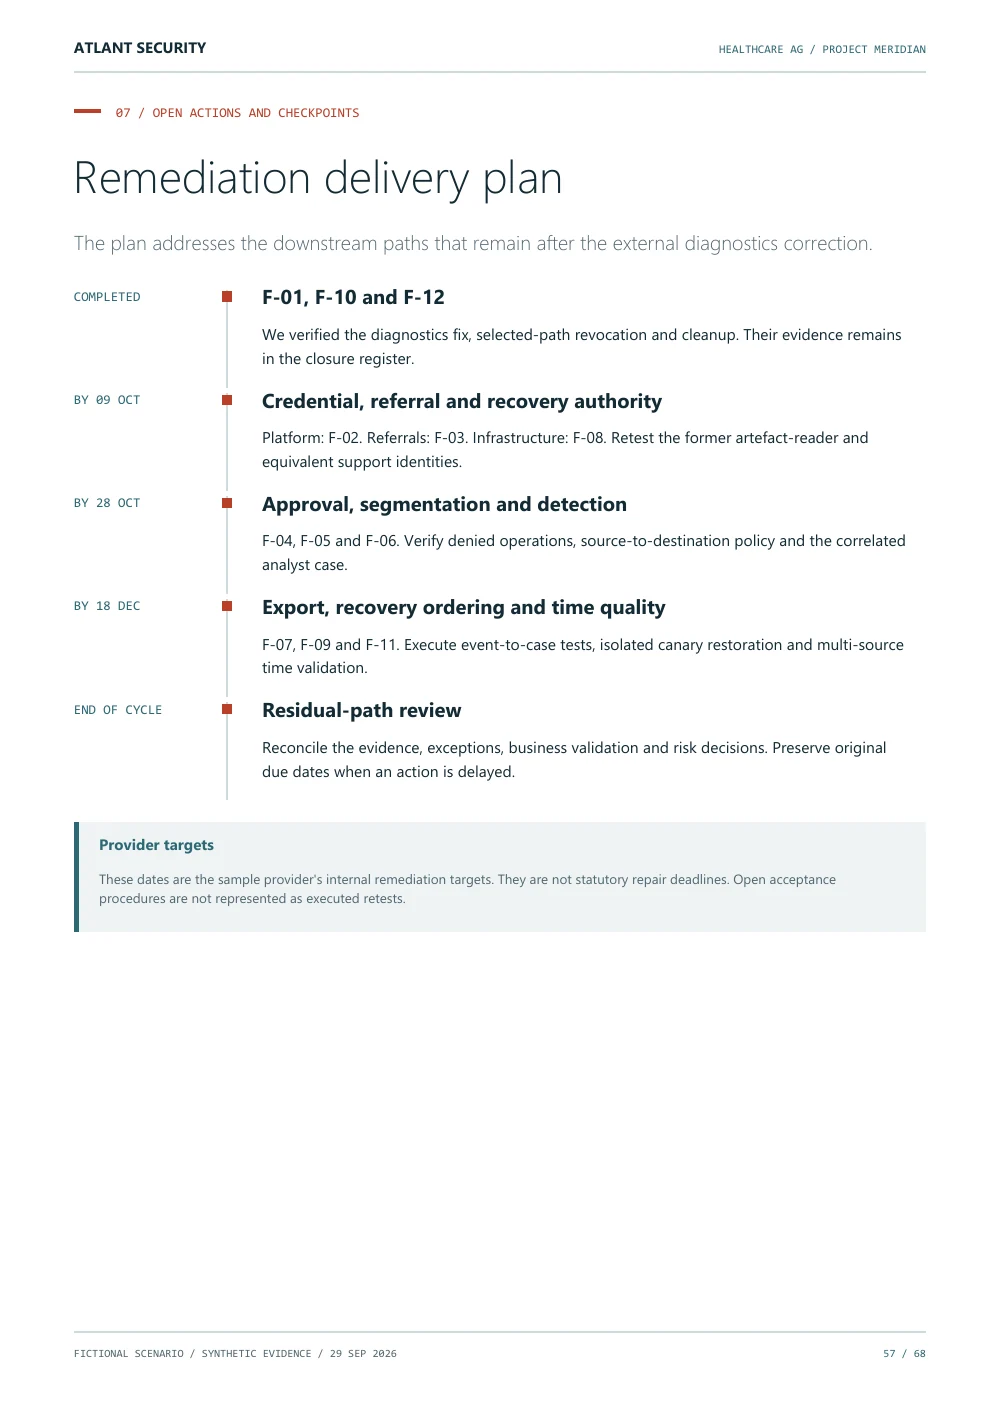
Three findings have recorded closure checks: command injection, session revocation and cleanup. Nine remain open, with dates for credential, referral and recovery authority, approval binding, segmentation, detection and supporting controls. These are fictional provider targets, not statutory repair deadlines.
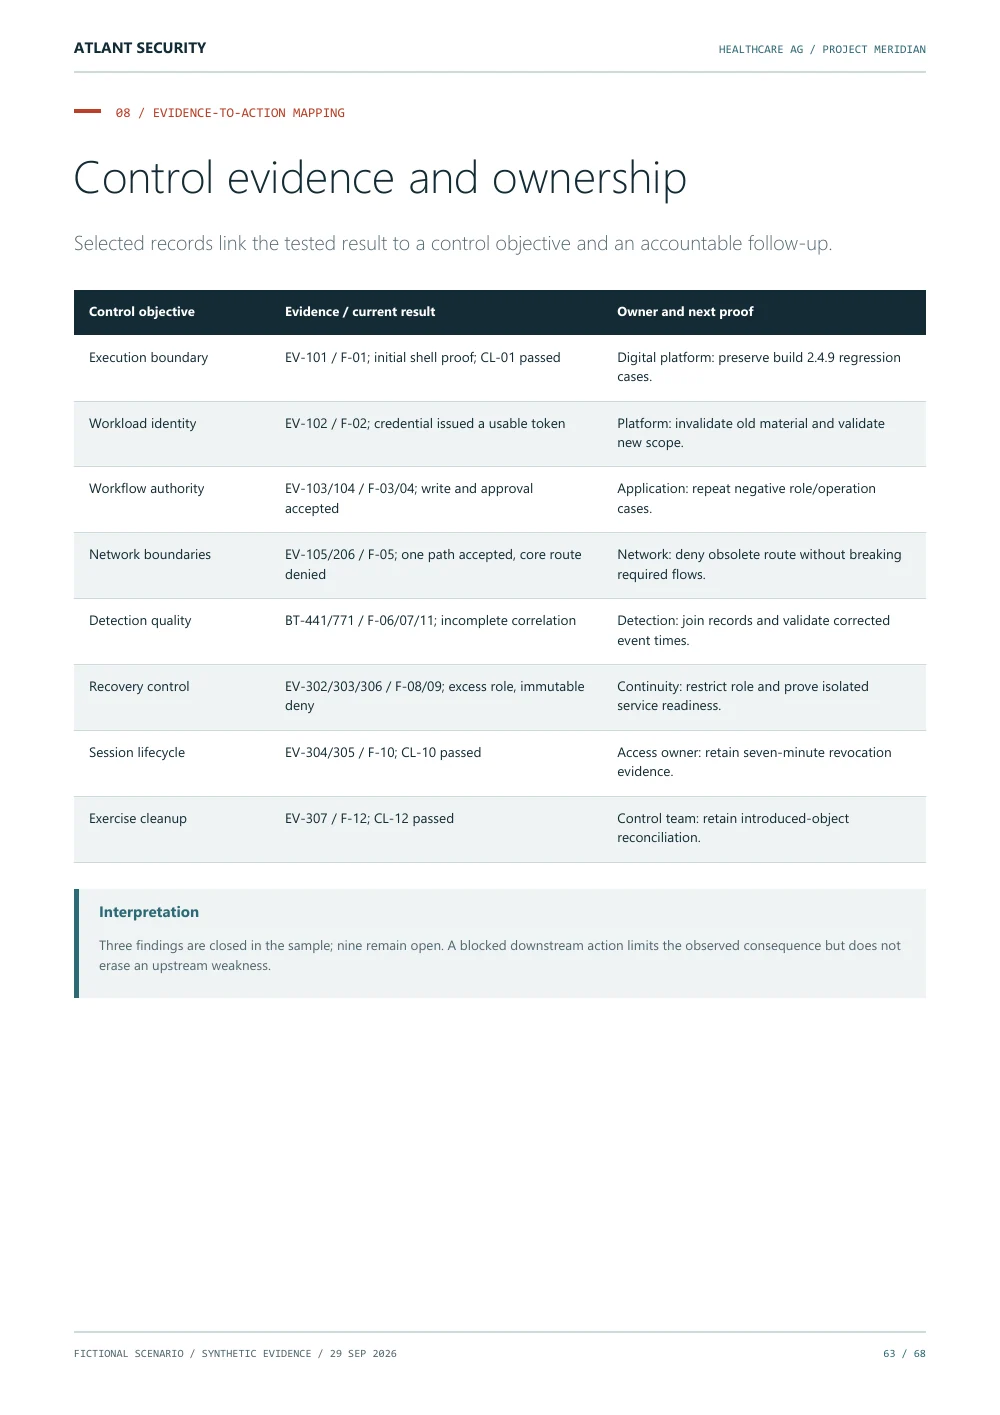
The mapping connects tested outcomes to control objectives, accountable owners, verification evidence and the limits of the assessment. It does not claim regulatory certification.
END OF THE PREVIEW
Get the complete report, including all twelve treatment plans and the full control mapping.
Continue to the full reportScroll within the preview, use the page index, or read each page’s text summary. Selected pages are public; the complete PDF is available after the form below.
INSIDE THE FULL REPORT
Business consequences, nine test objectives and the decisions for the board.
Scoped scan results, network and identity boundaries, WAF differentials and command-execution records.
Twelve technical findings with requests, responses, reproduction conditions and completed or pending retest records.
Sector requirements, evidence responsibilities, control mappings and assessment boundaries.
YOUR COPY OF PROJECT MERIDIAN
Get the complete 68-page sample Healthcare penetration testing report. A practical reference for scoping, procurement and the conversations that follow a test.
Free download. Available immediately after submitting.
No newsletter subscription.
Tell us where to direct any follow-up about your request.
Use the button below to save your copy. Your download access lasts for 15 minutes in this browser.
Download the 68-page PDFA fictional case study by Atlant Security.
Need an alternative format? Contact us.
No. Healthcare AG and every system, participant, event and result are fictional. The case is designed to demonstrate a realistic reporting approach without exposing any client information.
Healthcare security requirements depend on entity, location and processing. For EU organisations, assess NIS2 scope and national implementation alongside GDPR security obligations. For US covered entities and business associates, consider HIPAA separately. A pentest contributes technical evidence; it does not determine legal applicability or certify compliance. The fictional sample is not a compliance certificate.
One searchable 68-page PDF with bookmarks, vector architecture diagrams, HTTP and shell evidence, three execution records, twelve findings and treatment plans, a remediation roadmap and control mapping. The preview above shows eight selected pages from that same report.
Your download becomes available immediately in this browser. Atlant Security receives the details you submit and may follow up about your request and testing requirements. There is no automatic newsletter subscription.